Armor Advocates Governed Path for AI in Business Operations
News related to:Armor Defense Inc · 2 min read
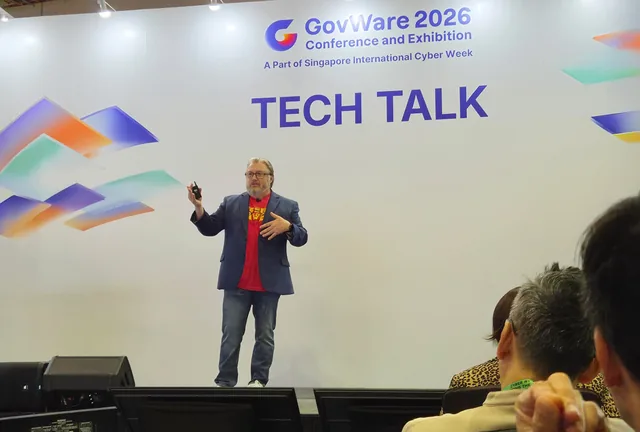
SINGAPORE, Oct. 14, 2026 /CourierPR/ -- Armor Defense Inc, the company that has secured regulated industries for over 17 years, is advocating for a governed path for artificial intelligence (AI) rather than a ban. This stance was articulated by Chris Drake, Armor’s founder and CEO, during a Tech Talk Spotlights session at GovWare 2026.
Drake emphasized that AI should complete useful business work automatically within policy. He highlighted that CISOs (Chief Information Security Officers) can enable this autonomy by resolving data classification, owning routing rules, and demanding auditable evidence. These measures are crucial as CISOs face pressure to facilitate AI innovation while safeguarding business operations, customer trust, and contractual commitments.
According to a February 2026 Protiviti AI Pulse Survey, 47% of large organizations reported incomplete visibility into employees' use of AI tools. This underscores the urgency for organizations to establish clear policies and controls around AI adoption. Drake pointed out that AI can arrive through employees and the tools they use, often bypassing traditional security checkpoints. He warned that banning AI is not a viable solution, as ignoring it can lead to breaches and security vulnerabilities.
Armor, which has been serving regulated industries since 2009, faced the same challenge. Drake explained that the company was concerned about sending customer data through public AI services where controls and audit evidence could not meet its customer commitments. To address this, Armor built a governed AI platform called Sovereign AI, which it now uses for its own operations. Sovereign AI is designed to provide a fully governed platform that allows organizations to leverage AI without creating undue risk to their data and regulatory obligations.
Drake outlined the principles behind Sovereign AI: knowing the data, preserving model choice, owning routing policies, controlling actions, and demanding full auditability. He urged CISOs to give the whole company useful, approved AI, thereby reducing the incentive for employees to use shadow AI. To grant an AI tool access, CISOs should ask three key questions: what can the tool touch, where can it send data, and can the organization control what it does?